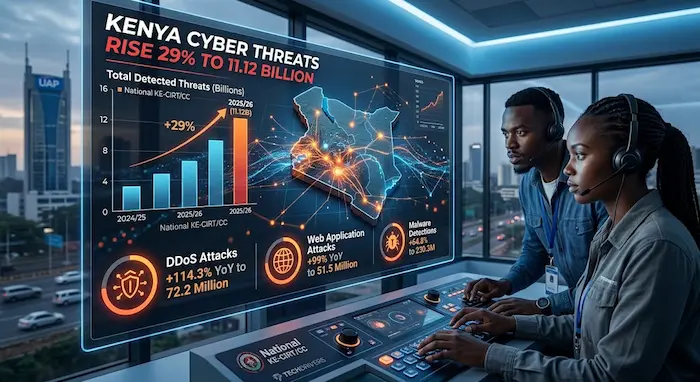

Kenya recorded a significant increase in detected cyber threats during the 2025/26 financial year, with the National Kenya Computer Incident Response Team Coordination Centre (National KE-CIRT/CC) detecting 11.12 billion cyber threats, up 29% from 8.62 billion recorded in the previous financial year.
The latest figures highlight the growing pressure on Kenya’s digital infrastructure as businesses, government services and consumers increasingly depend on online platforms.
Although the number of detected threats fell during the fourth quarter, the full-year figures show that cyber activity remained substantially higher than a year earlier.
Kenya Detected 2.36 Billion Cyber Threats in Q4
The National KE-CIRT/CC detected 2.36 billion cyber threats during the fourth quarter, representing a 30% decline from the 3.37 billion recorded in the previous quarter.
However, the quarterly decline does not change the broader annual trend.
Across the full 2025/26 financial year, detected threats reached 11.12 billion, compared with 8.62 billion in the preceding year.
The figures cover detected cyber-threat activity rather than confirmed cases in which attackers successfully compromised individual users or organizations. A high detection figure therefore should not automatically be interpreted as 11.12 billion successful attacks.
System Vulnerabilities Accounted for Most Detected Threats
System vulnerabilities remained the largest category by a significant margin.
The National KE-CIRT/CC recorded approximately 10.6 billion system vulnerability-related threats during the year, representing a 28.2% increase year on year.
The scale of this category shows why maintaining updated software, operating systems, applications and network infrastructure remains important for organizations operating online.
For businesses, an unpatched server, outdated application or vulnerable network device can create an entry point that attackers may attempt to exploit.
DDoS Attacks More Than Doubled
One of the biggest increases was recorded in distributed denial-of-service (DDoS) attacks.
DDoS activity increased by 114.3% year on year to 72.2 million attacks.
These attacks attempt to overwhelm websites, servers or online services with large volumes of traffic, potentially making legitimate services unavailable.
Interestingly, DDoS activity dropped sharply during the fourth quarter. The National KE-CIRT/CC recorded 819,325 DDoS attacks in Q4, down 90% from 8.2 million in the preceding quarter.
The quarterly pattern suggests that a substantial amount of the year’s DDoS activity occurred earlier in the financial year.
For Kenyan businesses that depend on websites, mobile applications, online payments or digital customer services, DDoS attacks can create operational and financial risks even when sensitive information is not stolen.
Web Application Attacks Nearly Doubled
Web applications also experienced a major increase in attacks.
The number of detected web application attacks rose 99% year on year to 51.5 million.
Unlike some broad network-level threats, web application attacks can directly target websites and online services.
The category also increased during the fourth quarter, rising by 43.7%.
This is particularly relevant to Kenyan businesses running e-commerce websites, customer portals, financial platforms and other internet-facing services.
Organizations should therefore treat website security as part of their broader cybersecurity strategy rather than relying only on antivirus software installed on individual computers.
Malware Detections Rose 64.8%
Malware was another major area of growth.
Detected malware activity increased 64.8% to 230.3 million during the financial year.
Malware can include different forms of malicious software designed to steal information, disrupt systems, monitor users or provide attackers with unauthorized access.
For ordinary users, the risk can begin with seemingly simple actions such as installing applications from untrusted sources, opening malicious attachments or clicking suspicious links.
Keeping devices updated and downloading software from trusted sources can reduce some of these risks.
Brute-Force Attacks Increased More Slowly
Brute-force attacks recorded a comparatively modest increase.
The National KE-CIRT/CC detected 132.2 million brute-force attacks, representing a 3.6% year-on-year increase.
These attacks involve repeated attempts to obtain access by guessing passwords or other credentials.
However, the number of warnings issued to users over brute-force activity increased much more sharply.
The Authority’s cyber advisories relating to brute-force attacks rose from approximately 5.5 million to 25.5 million, an increase of more than five times.
That difference could partly reflect broader monitoring and increased efforts to warn users and organizations about suspicious login activity.
Cyber Advisories Increased to 83.1 Million
The rise in detected threats was accompanied by a significant increase in cyber advisories.
The Communications Authority reported 83.1 million cyber advisories during the financial year, compared with 51.7 million the previous year.
That represents an increase of approximately 60.8%.
Web application attack advisories also increased significantly, reaching 40.5 million, up 110.5% year on year.
For organizations, the growing number of advisories highlights the importance of responding to security warnings rather than treating them as background technical information.
Kenya’s Cyber Threat Figures at a Glance
| Threat Type | Annual Total | Year-on-Year Change | Q4 Figure | Quarterly Change |
|---|---|---|---|---|
| System vulnerabilities | 10.6 billion | +28.2% | — | — |
| Malware | 230.3 million | +64.8% | — | — |
| Brute-force attacks | 132.2 million | +3.6% | — | — |
| Web application attacks | 51.5 million | +99% | — | +43.7% |
| DDoS attacks | 72.2 million | +114.3% | 819,325 | -90% |
Figures are detected cyber-threat activity reported by the National KE-CIRT/CC and should not be interpreted as the number of confirmed successful compromises.
What the Numbers Mean for Kenyan Businesses
The figures have practical implications for Kenyan businesses, particularly those increasingly moving operations online.
A small business with an online store, WordPress website, customer database or cloud-based business system can become part of the country’s wider digital attack surface.
Businesses should consider several basic measures:
Keep software updated
Security updates often address vulnerabilities that attackers may attempt to exploit. Organizations should maintain a process for updating operating systems, websites, plugins, applications and network equipment.
Use stronger authentication
Businesses should avoid relying on weak or reused passwords. Multi-factor authentication can provide an additional layer of protection for important accounts.
Protect internet-facing websites
Websites and web applications should be regularly monitored for vulnerabilities. Businesses using content-management systems should also keep themes, plugins and core software updated.
Back up important information
Backups can help organizations recover from incidents such as ransomware, accidental deletion or system compromise.
Train employees
Employees can become targets through phishing messages, malicious attachments and fraudulent login pages. Basic cybersecurity awareness can reduce the likelihood of successful social-engineering attacks.
Kenya’s .KE Domain Space Continues to Grow
The cybersecurity figures come as Kenya’s local domain ecosystem continues to expand.
By June 2026, registrations across the .KE domain space reached 129,140, representing a 3.7% annual increase.
Commercial .CO.KE domains remained the largest category, with 114,662 registrations, up 16% during the year.
Government .GO.KE domains increased 8.3% to 928.
The .MOBI.KE category recorded a much larger percentage increase, rising 113.9% to 77 registrations during the quarter. However, the percentage increase needs to be viewed in context because the category remains very small.
Meanwhile, .SC.KE domains, used by lower and middle-level educational institutions, declined by 4.2% over the year.
| Domain Category | Registrations | Change | Context |
|---|---|---|---|
| .KE | 129,140 | +3.7% annually | Overall .KE domain space |
| .CO.KE | 114,662 | +16% annually | Largest commercial category |
| .GO.KE | 928 | +8.3% annually | Government domains |
| .MOBI.KE | 77 | +113.9% quarterly | Small registration base |
| .SC.KE | Not specified | -4.2% annually | Education category |
Why Kenya’s Cybersecurity Numbers Matter
Kenya’s growing dependence on digital services means cybersecurity is becoming an issue beyond large technology companies and government institutions.
Banks, retailers, schools, startups, media organizations, healthcare providers and small businesses increasingly rely on websites, cloud systems, mobile applications and online accounts.
That creates more opportunities for legitimate digital services, but it also expands the potential attack surface.
The 11.12 billion detected threats should therefore be viewed as a signal of the scale of cyber activity being monitored across Kenya’s digital environment, rather than as a direct count of people or companies that were successfully hacked.
The sharp increases in malware, web application attacks and DDoS activity also show why cybersecurity needs to cover more than traditional computer viruses.
What Kenyan Internet Users Can Do
Individual users can take several practical steps to improve their security:
- Use unique passwords for important accounts.
- Turn on multi-factor authentication where available.
- Keep smartphones and computers updated.
- Avoid installing applications from unknown sources.
- Be cautious when clicking links received through SMS, email and social media.
- Never share one-time passwords or authentication codes.
- Check website addresses before entering login or payment information.
- Back up important files.
- Report suspicious activity through the appropriate channels.
Frequently Asked Questions
How many cyber threats were detected in Kenya?
The National KE-CIRT/CC detected 11.12 billion cyber threats during the 2025/26 financial year, up from 8.62 billion the previous year.
Did Kenya experience 11.12 billion successful cyberattacks?
No. The figure represents detected cyber threats and activity, not 11.12 billion confirmed successful compromises of users or organizations.
Which cyber threat increased the most?
Among the categories reported, DDoS attacks recorded the largest year-on-year increase at 114.3%, reaching 72.2 million.
How many malware threats were detected?
Kenya recorded approximately 230.3 million malware detections, representing a 64.8% increase year on year.
Why are web application attacks important?
Web applications are directly exposed to the internet and can provide access to websites, databases and online services when vulnerabilities are exploited. Their 99% annual increase makes website security particularly relevant for businesses operating online.
What is a brute-force attack?
A brute-force attack involves repeated attempts to guess passwords or other login credentials in an effort to gain unauthorized access to an account or system.
Conclusion
Kenya’s 11.12 billion detected cyber threats in 2025/26 underline the growing scale of activity targeting the country’s digital environment.
The most significant increases were not limited to general system vulnerabilities. Malware detections rose sharply, web application attacks nearly doubled, and DDoS activity more than doubled over the year.
For Kenyan businesses and internet users, the lesson is practical: cybersecurity cannot be treated as a problem reserved for large technology companies.
As more services move online, securing websites, devices, accounts and digital infrastructure will become increasingly important to keeping Kenya’s growing digital economy reliable and resilient.
