
Kenya’s non-profit sector handles a huge amount of personal information.
An organisation working with children may collect names, ages, locations and family information. A human-rights organisation may maintain case files involving survivors of violence. A health-focused charity may process medical information, while another organisation may collect identification details, phone numbers and financial information from beneficiaries.
That makes data protection more than an IT issue.
It can affect the privacy, safety and trust of the people non-profit organisations are trying to help.
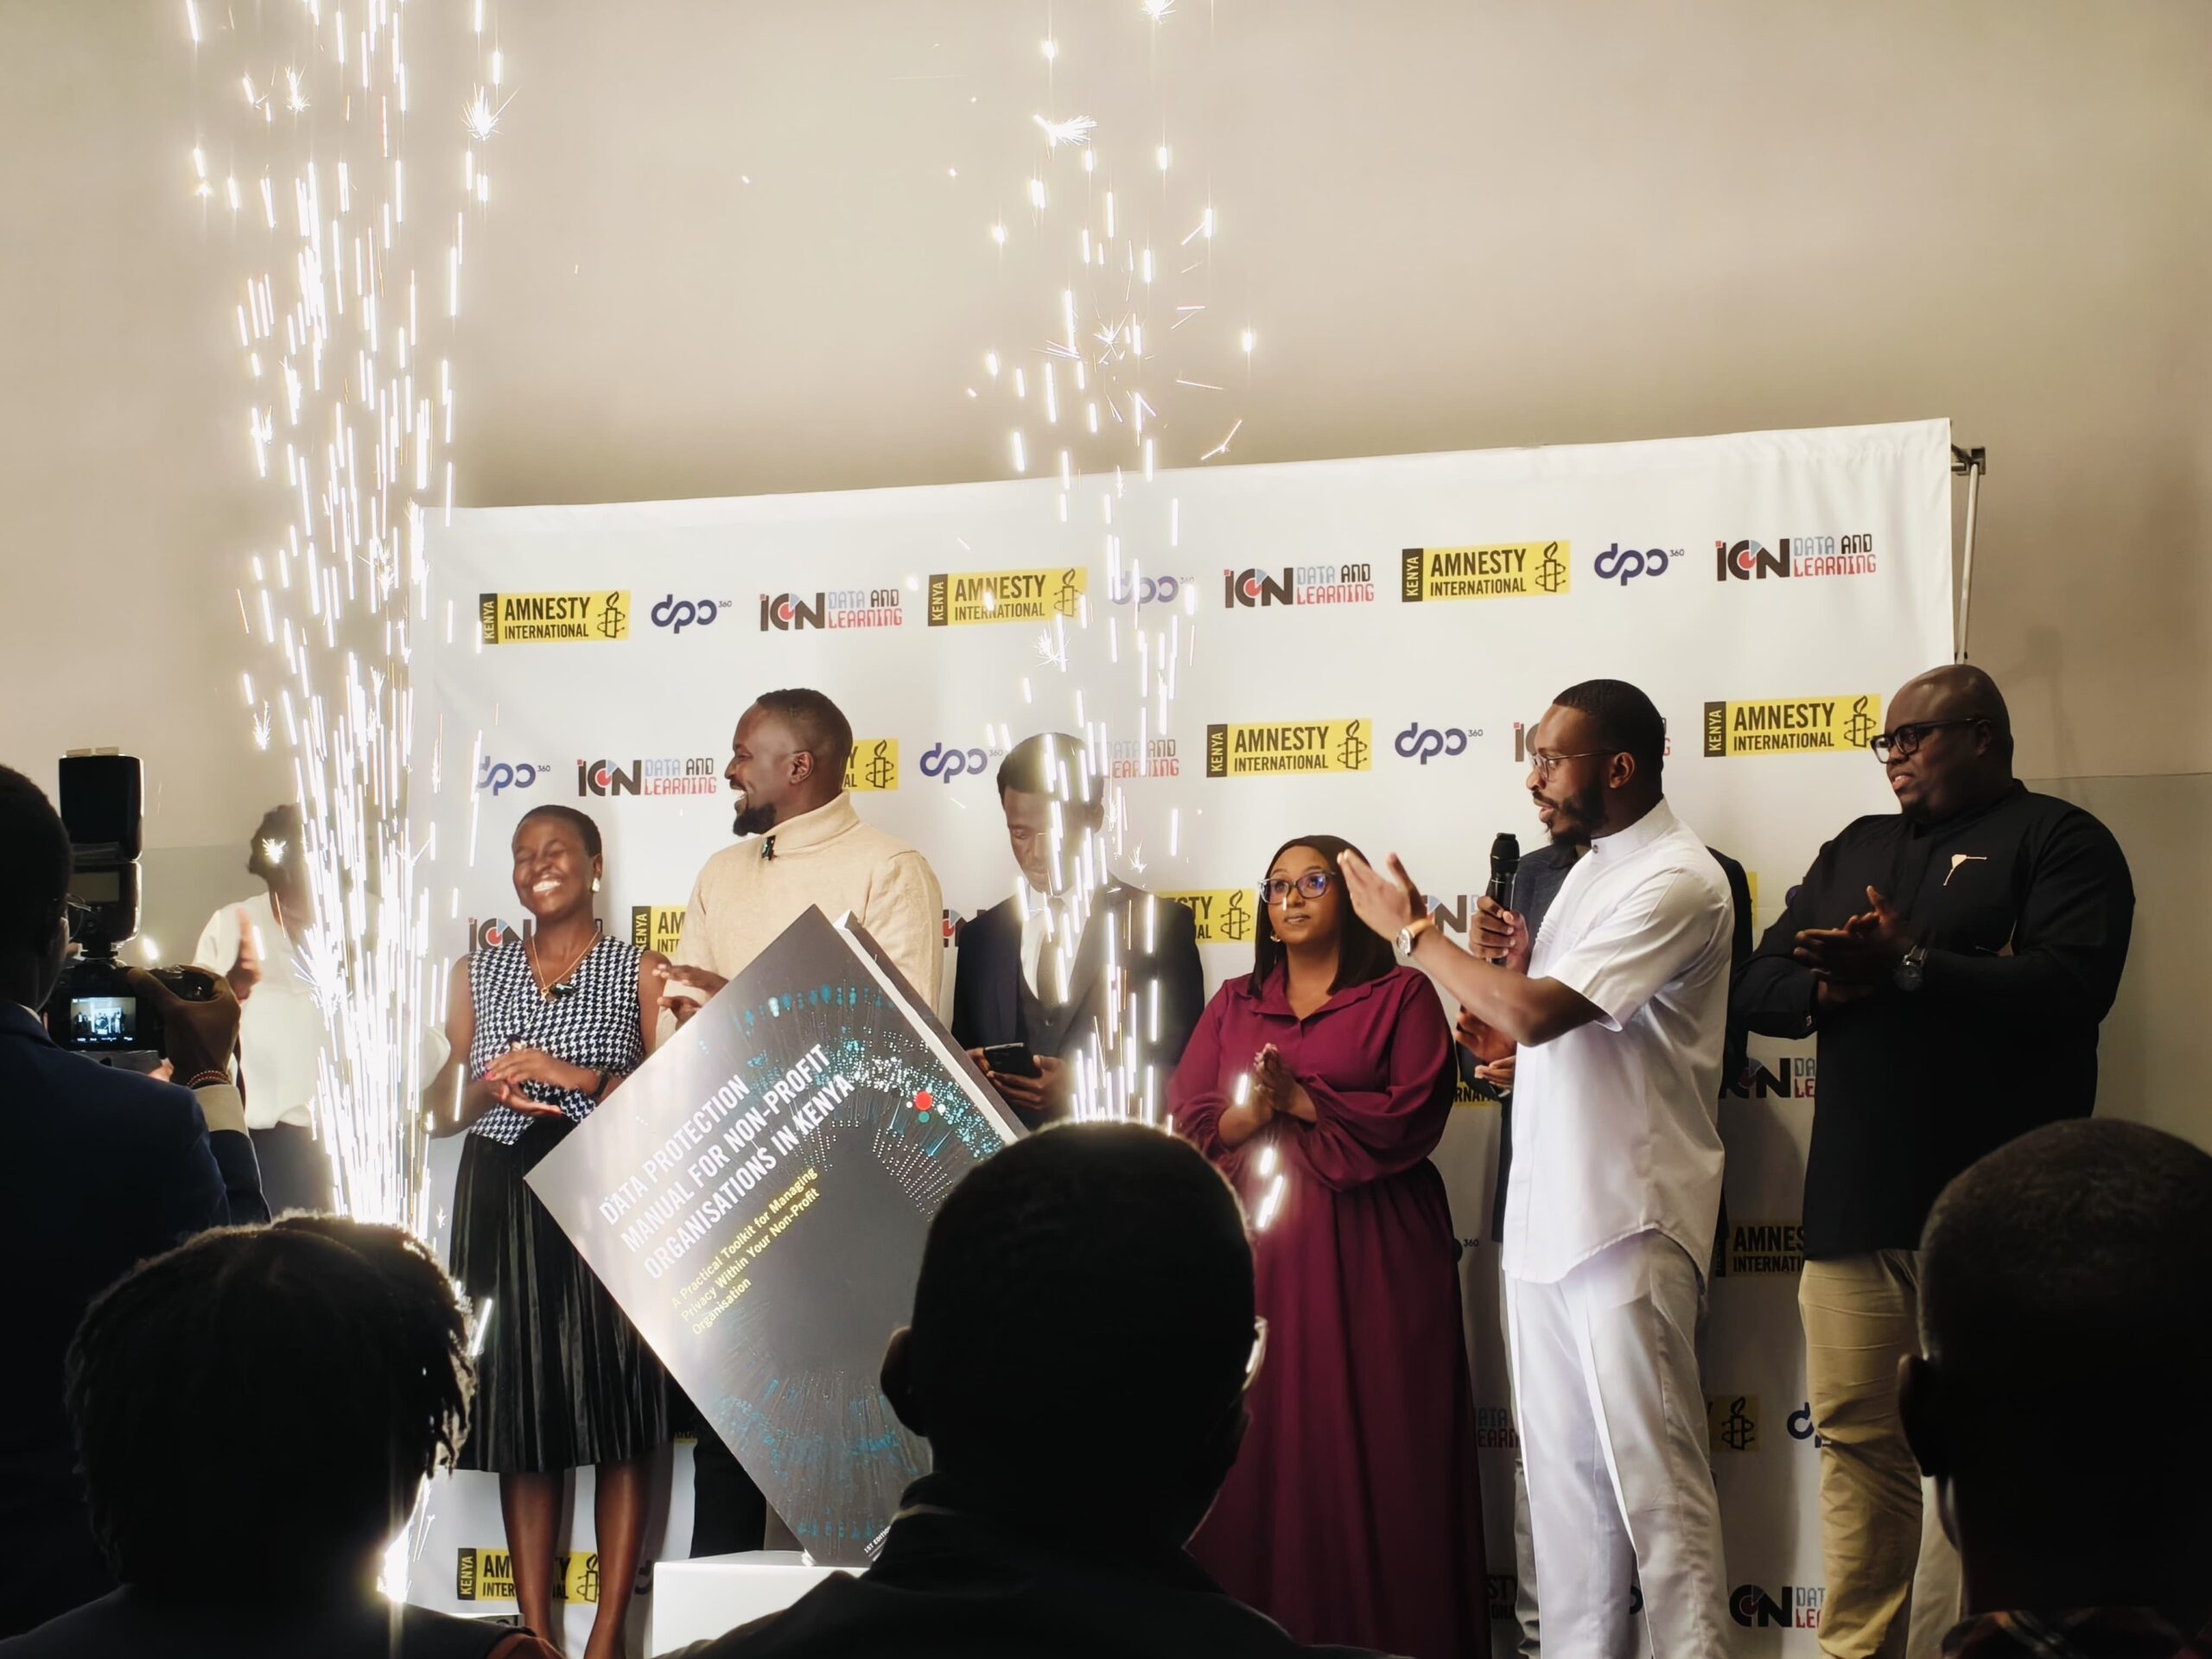
A new Data Protection Manual for Non-Profit Organisations in Kenya, published by Amnesty International Kenya on September 25, 2026, is designed to help organisations translate Kenya’s data-protection requirements into practical procedures.
The first-edition 2026 manual was developed by Amnesty International Kenya in collaboration with DPO 360 Africa Limited and ICON Data and Learning Labs.
Why Data Protection Matters for Kenyan Non-Profits
Non-profit organisations often operate in environments where the information they collect can be highly sensitive.
Consider a community organisation supporting survivors of gender-based violence.
A beneficiary record could contain:
- Full name
- Telephone number
- Location
- Identification information
- Health information
- Details about an incident
- Information about family members
- Photographs
- Case notes
- Referrals to other organisations
If such information is exposed, the consequences can go beyond inconvenience.
It could expose a vulnerable person to harassment, discrimination, financial fraud, intimidation or other risks.
The new manual therefore approaches data protection as both a legal and operational responsibility.
Amnesty International Kenya says the toolkit is intended to help organisations connect the requirements of the Data Protection Act, 2019 with day-to-day activities such as beneficiary intake, surveys, case management, cloud storage and information sharing.
Kenya’s Data Protection Framework
Kenya’s data protection framework is anchored in Article 31 of the Constitution of Kenya, which protects the right to privacy.
The Data Protection Act, 2019 provides the main statutory framework governing the processing of personal data in Kenya.
The Office of the Data Protection Commissioner (ODPC) identifies several rights belonging to data subjects, including the right to be informed about how their personal data will be used, access their personal data, object to processing, and seek correction or deletion of certain inaccurate or misleading information.
For non-profits, this means collecting someone’s information is not simply a matter of creating a spreadsheet or filling out an online form.
The organisation needs to consider why the information is being collected, what it will be used for, who can access it, how long it should be retained and what happens when it is no longer required.
What the New Manual Covers
The manual is structured as a practical toolkit rather than simply a discussion of privacy law.
Among the areas covered are privacy concepts, Kenya’s Data Protection Act, lawful bases for processing, consent, data-subject rights, data breaches, cross-border transfers and the creation of organisational privacy programmes.
1. Understanding the Difference Between Privacy, Data Protection and Security
These terms are often used interchangeably, but they address different issues.
Privacy concerns a person’s control and rights regarding their personal information and private life.
Data protection concerns the rules and processes governing how personal data is collected, used, stored and shared.
Data security focuses on technical and organisational measures used to protect information from unauthorised access, loss, alteration or destruction.
A non-profit can therefore have strong cybersecurity tools and still have poor data-protection practices.
For example, an organisation might securely store a database but collect far more information than it actually needs.
Security alone does not solve that problem.
2. Data Minimisation
One of the important principles highlighted in the manual is data minimisation.
The basic idea is straightforward: organisations should avoid collecting personal information that is unnecessary for the purpose for which it is being processed.
Imagine a Kenyan charity organising a food-distribution programme.
If the organisation needs a beneficiary’s name, contact information and location to coordinate delivery, it should consider whether it actually needs additional information such as unrelated family details, copies of documents or extensive personal histories.
Collecting less information can reduce the potential impact of a future breach.
3. Purpose Limitation
Information collected for one reason should not automatically become available for unrelated purposes.
For example, if an NGO collects a beneficiary’s phone number to coordinate an appointment, that does not automatically mean the number should be added to a marketing database.
Organisations need to establish clear purposes for processing personal data and communicate those purposes appropriately.
4. Accuracy and Storage
The manual also addresses data accuracy and storage limitation.
Incorrect information can cause real-world problems.
A wrong telephone number can prevent a beneficiary from receiving assistance. An inaccurate medical record could potentially affect services. An outdated address could result in sensitive correspondence being sent to the wrong person.
Organisations therefore need processes for correcting inaccurate information and deciding how long different categories of data should be retained.
Data Subject Rights Matter Too
A person whose information is being processed is not simply a record in an NGO database.
Under Kenya’s data-protection framework, data subjects have specific rights.
The ODPC lists rights including being informed about the use of personal data, accessing personal data held by a controller or processor, objecting to processing, correcting false or misleading information and seeking deletion of false or misleading data.
The new manual provides guidance on handling Data Subject Requests (DSRs) and highlights statutory timelines, including a 14-day timeframe discussed in the publication.
For an NGO, this means there should be a clear internal process for receiving, verifying, recording and responding to requests.
A staff member should not have to improvise when a beneficiary asks:
“What information do you have about me?”
What Happens When an NGO Suffers a Data Breach?
This is one of the areas where cybersecurity and data protection meet directly.
Suppose an organisation’s laptop containing beneficiary records is stolen.
Or a staff member accidentally sends a spreadsheet containing personal information to the wrong email address.
Or attackers compromise an organisation’s cloud account.
These incidents can potentially become personal-data breaches.
Kenya’s Data Protection Act provides requirements around breach notification. Where a data controller determines that a personal-data breach is likely to result in a risk to the rights and freedoms of a data subject, the Act provides for notification to the Data Commissioner within 72 hours of becoming aware of the breach, subject to the Act’s requirements.
The Act also provides that a data processor that becomes aware of a personal-data breach should notify the data controller without delay and, where reasonably practicable, within 48 hours.
This is why organisations need an incident-response procedure before something goes wrong.
Waiting until after a breach to decide who should be contacted can waste valuable time.
Why Data Protection Officers Matter
The manual also covers the responsibilities of Data Protection Officers and organisational compliance structures.
For organisations that require such arrangements, the DPO function can help coordinate privacy responsibilities across departments.
A privacy programme should not exist only on paper.
Staff collecting information in the field, programme teams managing beneficiaries, finance departments handling donor records and IT teams managing systems can all affect how personal data is processed.
That makes staff training an important part of compliance.
Cross-Border Data Transfers and Cloud Services
Kenyan organisations increasingly use cloud platforms for email, file storage, accounting, customer relationship management, surveys and collaboration.
That creates another important question:
Where is the data being processed or stored?
The manual includes guidance on cross-border transfers, adequacy mechanisms, Standard Contractual Clauses (SCCs), cloud services and Transfer Impact Assessments (TIAs).
For example, a Kenyan NGO might collect beneficiary information through an online form and store the resulting database on an international cloud platform.
The organisation should understand the privacy and contractual arrangements surrounding that processing rather than treating cloud storage as automatically risk-free.
A Practical Example: A Kenyan Community NGO
Consider a fictional organisation called Mwangaza Community Initiative operating in Nairobi and supporting young people from low-income communities.
Its staff collect:
- Names
- Phone numbers
- Age
- Residential area
- Emergency contacts
- School information
- Programme participation records
The organisation could build a basic privacy programme around several questions.
Before collecting information
Ask:
Why do we need this information?
If a piece of information is not necessary, the organisation should consider whether collecting it is justified.
During collection
Tell the person:
- What information is being collected
- Why it is being collected
- How it will be used
- Who may receive it where relevant
- How they can exercise applicable rights
During storage
Limit access to people who actually need the information.
Use appropriate passwords, access controls, backups and security measures.
When sharing information
Confirm that the proposed sharing has an appropriate legal basis and is consistent with the stated purpose.
When information is no longer needed
Apply the organisation’s retention and deletion procedures rather than keeping every record indefinitely.
This kind of workflow turns privacy from a legal document into an operational process.
A 13-Part Privacy Programme
One notable part of the manual is its operational approach to setting up a privacy programme.
The publication describes 13 core components, including Records of Processing Activities (ROPA), data classification and incident management.
For a Kenyan non-profit, a practical programme can start with an inventory of the information it already holds.
For example:
| Data category | Possible examples | Key question |
|---|---|---|
| Beneficiary data | Names, contacts, programme records | Why is it needed? |
| Case information | Complaints, case notes, referrals | Who can access it? |
| Health information | Medical records or health details | Is additional protection required? |
| Staff information | HR and payroll records | How long should it be retained? |
| Donor information | Names, contacts, contribution records | What is the purpose? |
| Digital credentials | Account and system access information | How is access protected? |
The exact requirements will depend on the organisation, the data involved and the circumstances of processing.
What This Means for Kenyan NGO Staff
Data protection is not only the responsibility of the IT department or legal team.
A programme officer can accidentally expose personal data.
A field worker can lose a phone containing beneficiary information.
A finance employee can send a spreadsheet to the wrong recipient.
A communications officer can publish a photograph without properly considering the privacy implications.
A volunteer can download sensitive records onto a personal device.
That means privacy training needs to reach the people actually handling information.
What Ordinary Kenyans Should Know
The manual is written primarily for non-profit organisations, but its subject matter also offers useful lessons for people who provide personal information to organisations.
Before giving an organisation your information, consider asking:
Why do you need it?
How will you use it?
Who will have access to it?
How long will you keep it?
What happens if there is a breach?
People should also be cautious about sending identification documents, health information or other sensitive records through unsecured channels unless there is a legitimate reason to do so.
Kenya’s Growing Cybersecurity Challenge
The need for stronger privacy practices comes as Kenya’s digital environment continues to face significant cybersecurity activity.
TechDrivers recently reported that the National KE-CIRT/CC detected 11.12 billion cyber threats during the 2025/26 financial year, up from 8.62 billion the previous year. The figures represent detected cyber threats rather than 11.12 billion confirmed successful compromises.
For organisations holding sensitive personal information, cybersecurity and data protection therefore need to work together.
A privacy policy cannot compensate for an organisation that leaves accounts unprotected.
Likewise, sophisticated cybersecurity tools cannot fix a process that collects unnecessary personal information or shares it without proper controls.
Related TechDrivers Articles
If you want to understand the wider cybersecurity risks facing Kenyan internet users, read our related guides:
- What Happens to Your Data After You Delete an App?— deleting an application does not necessarily mean every piece of associated information immediately disappears.
- How SIM-Swap Fraud Works in Kenya and How to Protect Yourself — explains how attackers can exploit mobile-number-based authentication.
- How to Protect Your M-PESA Account From Fraud in Kenya — practical security measures for protecting mobile-money accounts.
- How Facebook Marketplace Scams Work in Kenya and How to Avoid Them — looks at common risks facing people buying and selling online.
- How Kenya’s Cyber Threats Rose to 11.12 Billion — examines the latest national cybersecurity threat figures.
These topics form part of the bigger question facing Kenya’s digital economy: how do we make digital services useful without treating people’s personal information as an afterthought?
Frequently Asked Questions
What is the Kenya data protection manual for non-profits?
It is a practical 2026 toolkit developed for non-profit organisations operating in Kenya. It explains privacy, data protection, lawful processing, data-subject rights, breach management, cross-border transfers and privacy-programme implementation.
Who published the manual?
The manual is an initiative of Amnesty International Kenya and was developed in collaboration with DPO 360 Africa Limited and ICON Data and Learning Labs.
Who can benefit from the manual?
It is particularly relevant to NGO leaders, boards, Data Protection Officers, compliance teams, programme officers, field staff, monitoring and evaluation teams and IT administrators.
What rights do data subjects have in Kenya?
The ODPC identifies rights including being informed about the use of personal data, accessing personal data, objecting to processing, correcting false or misleading information and seeking deletion of false or misleading information.
How quickly must a qualifying personal-data breach be reported?
Kenya’s Data Protection Act provides a 72-hour notification requirement to the Data Commissioner in circumstances covered by the Act. The Act also addresses notification responsibilities between data processors and controllers.
Does data protection only apply to large NGOs?
No. Organisations should assess their obligations based on the nature and circumstances of their data processing rather than assuming privacy compliance is only a concern for large organisations.
Why is data minimisation important?
Collecting only information that is necessary for a legitimate purpose can reduce the amount of personal data an organisation has to protect and can limit the potential impact of a data breach.
Does using Google Drive or another cloud service automatically make data compliant?
No. Cloud storage is a technology choice, not a complete data-protection programme. Organisations need to consider how personal information is processed, stored, accessed and transferred, including applicable requirements for cross-border processing.
Conclusion: Data Protection Has to Become an Everyday Practice
Kenya’s non-profit organisations often work with people who may already be in vulnerable circumstances.
That makes the information they hold particularly important to protect.
The new Data Protection Manual for Non-Profit Organisations in Kenya provides a practical framework for organisations trying to move from general awareness of privacy law to concrete procedures for collecting, using, storing, sharing and deleting personal information.
The bigger lesson extends beyond NGOs.
As Kenyan organisations move more services, records and interactions online, personal data is becoming an increasingly important part of everyday operations.
Protecting that data requires more than a privacy policy buried on a website.
It requires trained staff, controlled access, clear retention policies, appropriate security measures, documented procedures and a plan for responding when something goes wrong.
For non-profits, that is ultimately about more than compliance.
It is about protecting the people who trusted the organisation with their information.
